Security strategy
Set the priorities, investment choices and accountability for a security programme that supports the business.
Discuss security strategyFeatured session
Architecting Response Capabilities for AI agents and AI-on-AI Attacks
Designing detection, forensics, and response for environments where AI agents can be both targets and attackers.
The lab opens on GitHub. Public access is being prepared.
AI. Cloud. Enterprise security.
I lead enterprise security programmes and advise on AI and cloud risk, connecting business priorities, technical decisions, and operational execution.
15+ years of experience
Teams across 10 countries
Finance, telecoms and critical infrastructure, including operational technology.
01 / Perspective
I’ve owned security programmes at global enterprise scale, managed security professionals, and led across teams and security operations. That responsibility shapes how I approach every security decision.
Start with business priorities. Make risk and trade-offs explicit. Set clear ownership, then give teams the direction and support to deliver. Security strategy has to work in day-to-day operations and under pressure.
For executive teams making security decisions through growth, change and regulatory scrutiny.
Set the priorities, investment choices and accountability for a security programme that supports the business.
Discuss security strategySupport security leaders and executive teams with independent advice, executive reporting and clear accountability across their security programmes.
Discuss security leadershipReview governance, risk and compliance across AI adoption and cloud environments. Define decision rights, control priorities and the evidence needed for assurance.
Discuss AI & cloud GRC“His knowledge of cloud solutions and corporate architecture was a great contribution to the successful ending of the project.”
“Under pressure he stays clear about who decides what. During a major incident he gave us direction and room to work.”
02 / Writing
ISACA / 2024
How everyday habits shape a resilient security culture.
Read the articleTechnical reviewer / 2023
Author: Jeroen Mulder
BPB Publications
Technical review of a guide to managing multi-cloud environments, including security, access management and compliance.
View the book03 / Speaking
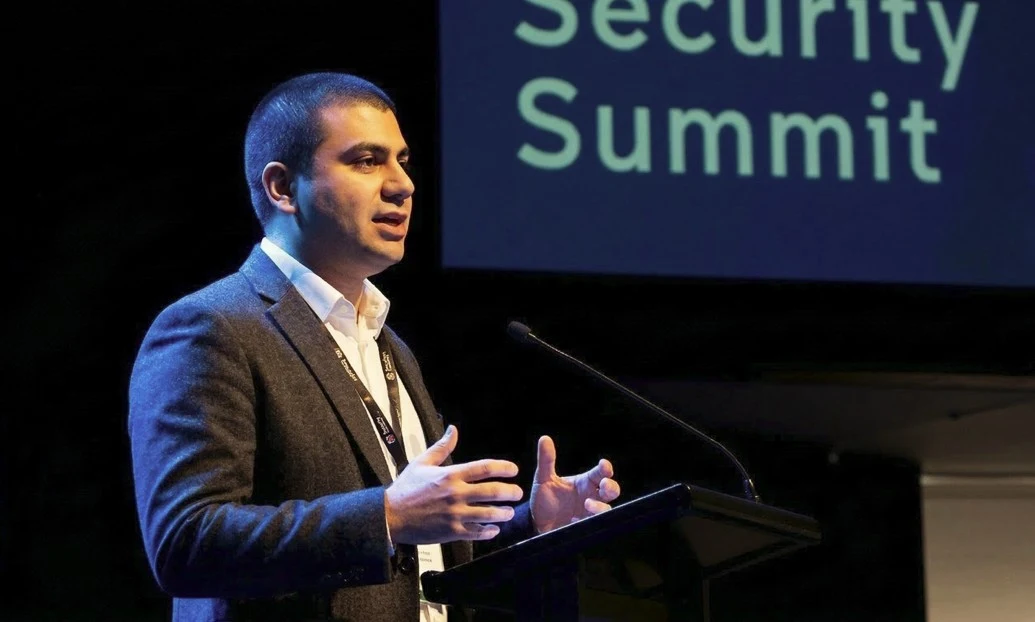
Conference talks on AI risk, cloud architecture, and incident response, connecting technical choices with their consequences for the organisation.
MYCPE ONE · Accounting in the Digital Age: 2026 and Beyond
Recognition · MYCPE ONE
Award winner
View recognitionISC2 Security Congress
Cloud Computing · Prague
With Pavel Krejsa
European Identity & Cloud Conference
Talk titles are shown in their original published language.
04 / Connect
Connect with me on enterprise security, AI and cloud risk, or leading security teams. For advisory work and speaking invitations, contact me directly.
Connect on LinkedInSave my details to your phone or computer. No app or account needed.
Save my contactOpen the contact file, then confirm “Add contact” on your device.